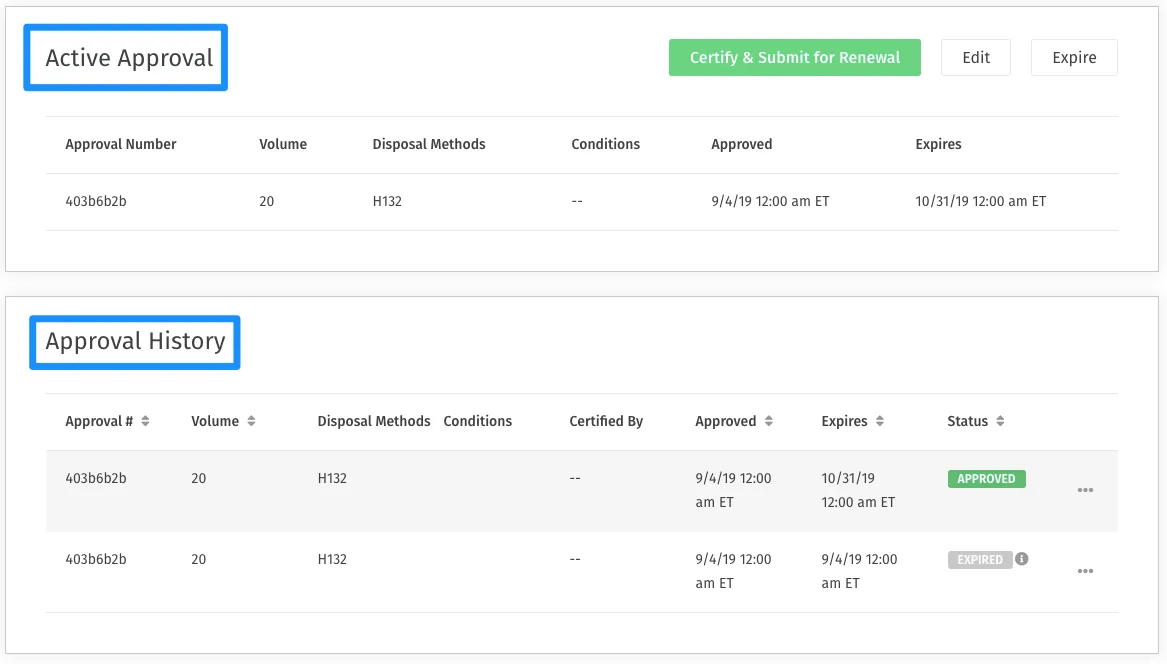
| Waste-stream approval and renewal | Documented by vendor | Custom profiles, supporting documents, approval history and expiry/renewal communication are described. Confirm the required classification inputs and receiving-facility review; a profile is not an independent waste determination. Waste profiles and approvals, no pricing page : checked 26 September 2026 |
|---|
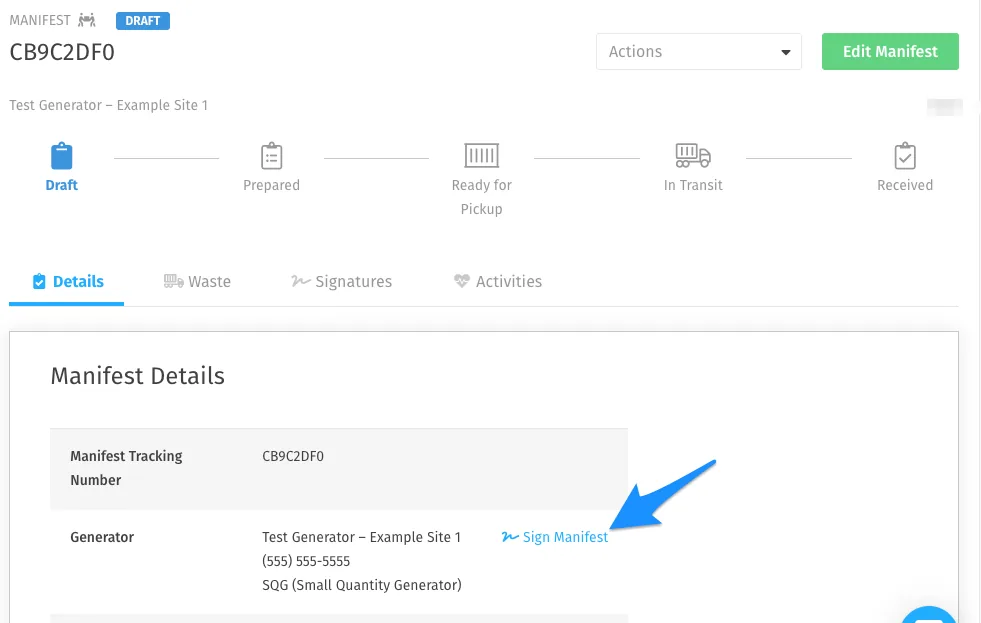
| Manifest preparation and party signatures | Documented by vendor | The manifest offering describes linked waste streams, transporter details, signatures and printable outputs. Hazardous and non-hazardous workflows have different conditions; demonstrate the one being purchased. Manifest software and signature workflow |
|---|
| US EPA status and correction handling | Depends on scope | Wastebits documents a mapping between its own status and RCRAInfo status. Post-signature corrections require appropriate permissions and further acknowledgement. Demonstrate both systems’ records and the responsible signer, rather than treating a saved edit as a completed correction. Hybrid manifest status mappingCorrections before and after transportEPA connection setup and user roles |
|---|
| Scale-ticket linkage | Depends on scope | Scale-house tools can link weighing records with approved profiles and manifests. Confirm the scale interface, units, identifiers and separate access to commercial details in the proposed configuration. Scale-house records and integrations |
|---|
| Facility data export | Depends on scope | The export help article is for Facility Portal Admins and Facility Site Admins at facility-site level. It covers waste streams, scale tickets and manifests. Generator access, attachments, signatures and a complete history package require separate confirmation. Facility export permissions and scope |
|---|
| Disconnected work and other jurisdictions | Not verified | The reviewed sources do not establish offline signatures/sync or a complete UK or EU regulatory interface. Use the exact country, waste type, transport parties and connection scenario in the demo. |
|---|
| Ordered non-hazardous signatures and delegated signing boundary | Depends on scope | The non-hazardous manifest guide documents an ordered Generator, Transporter and Facility signature sequence and says a user in the Generator or Service Provider company can sign for the Generator. These are non-hazardous workflow rules and should not be transferred to Hybrid EPA e-Manifests. Confirm signer identity, authority evidence, proxy policy, timestamp handling and the audit record for each party. Ordered non-hazardous manifest signatures and signing-party boundary : checked 29 September 2026 |
|---|
| Manifest attachment storage with company visibility choices | Depends on scope | Wastebits documents manifest uploads with visibility choices for all participating companies, facility and billing companies, or only the uploading facility company, across several file types. Confirm who may change visibility or delete a document, whether prior versions and access events remain auditable, malware controls, storage limits, retention and post-contract export. This is document storage, not evidence of an immutable regulatory archive. Manifest attachment storage and company-level visibility choices : checked 29 September 2026 |
|---|
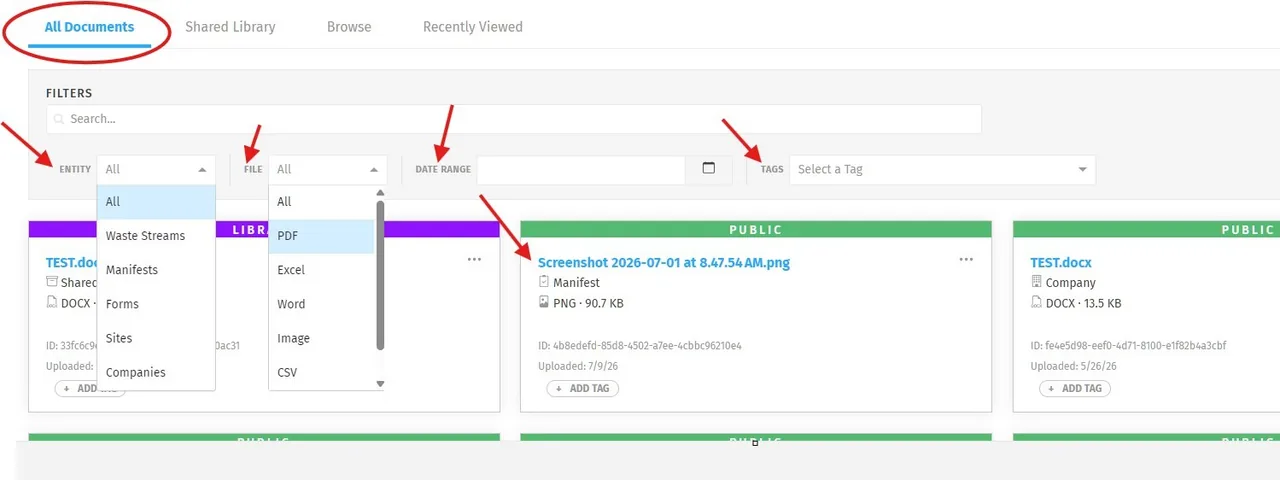
| Cross-record document search and shared library | Depends on scope | The 2026 Document Hub supports permission-filtered browsing, search and filters across documents attached to waste streams, manifests, forms, sites and companies, plus a portal shared library. Upload and delete controls depend on permissions. Confirm that users cannot discover restricted metadata, and verify versioning, audit history, retention, legal hold and complete export because those controls are not established by the guide. Document Hub search, entity scope, shared library and permission-dependent actions : checked 29 September 2026 |
|---|
| Two-factor authentication | Depends on scope | Wastebits documents email-code and authenticator-app verification, backup codes, optional every-login prompts and portal-wide enforcement. Confirm administrator roles, recovery and support override, enforcement for external companies, session timeout, audit events and compatibility with any quoted SSO. This feature does not by itself establish a security certification or complete identity-governance program. Portal-level and user-level two-factor authentication options : checked 29 September 2026 |
|---|