Exiger

    Exiger's 1Exiger platform covers supply chain risk, third-party risk management and due diligence. Its modern slavery article describes a knowledge graph of suppliers and third parties mapped to products down to raw materials, forced labour data, and sub-tier visibility beyond Tier 1.

    Exiger price on record: Quote-based · No amount published · Sources checked · See pricing

    Evidence: Researched profile

    Built from vendor sources checked ; AI-assisted drafting. Documentation review, not a hands-on test. How pages are made

    Who is Exiger for?

    Large organisations and public-sector buyers needing sub-tier forced labour mapping inside a broader supply chain risk programme. A broad enterprise risk platform; modern slavery statement preparation, remediation records and worker channels need to be demonstrated rather than assumed.

    Watch for: Enterprise scope; statement workflow needs a demo.

    Sources checked .

    Product tour

    Vendor visuals—not a QHSEtech hands-on test.

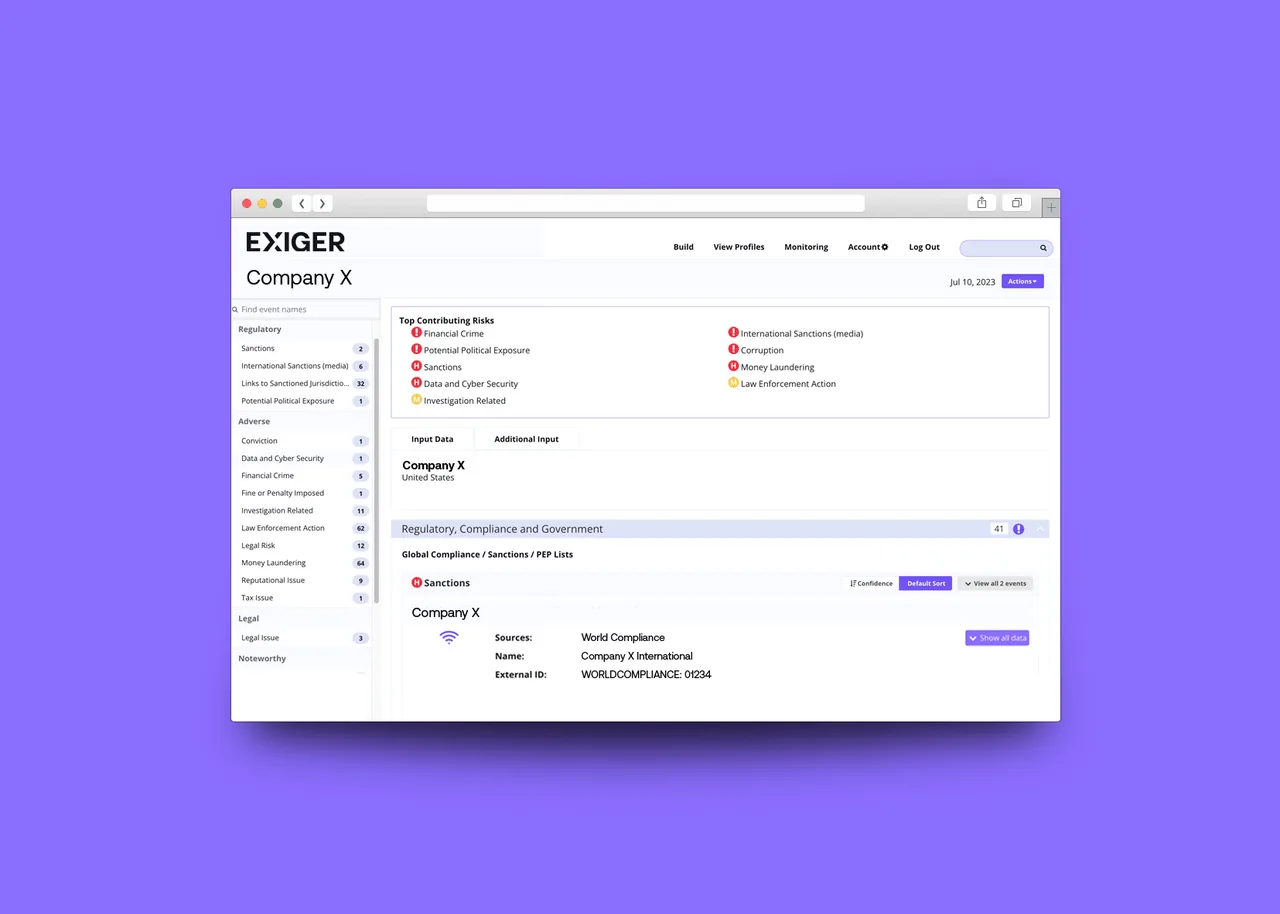
    Browser window showing an Exiger risk profile for Company X with top contributing risks and sanctions results

    Due diligence risk profile (sample company)

    Source

    Capabilities and scope

    Exiger provides the 1Exiger supply chain and third-party risk platform, which its site now presents as 1EXIGER.AI. This profile covers its forced labour and modern slavery supply chain mapping use. The about page states a 2013 founding and names no owner; a 10 September 2026 Exiger press release names Carlyle, Insight Partners and JMI Equity as investors and refers to a $1.2 billion investment they led in 2023.

    Exiger capabilities, evidence status and source links
    CapabilityEvidenceScope and source
    Forced labour supply chain mappingDocumented by vendor

    The vendor's article describes a knowledge graph representing suppliers and third parties and mapping products down to raw materials, combined with forced labour and supply chain data.

    Modern slavery tools article, checked 5 November 2026
    Nth-tier supplier identification and risk scoringDocumented by vendor

    The supply chain risk page states that the platform identifies nth-tier suppliers, applies risk scores and traces their data sources, with dashboards and ongoing monitoring. It does not give the tier depth achieved for a given product category, so test this with your own bill of materials.

    Exiger supply chain risk management, checked 5 November 2026
    UFLPA-specific forced labour mappingDepends on scope

    The UFLPA page describes four steps: risk source identification, network mapping, scoring and tagging, and continuous monitoring, using Chinese government, geospatial and trade data. Its stated scope is Xinjiang and related Chinese supply chains for US importers, so check coverage for other regions and regimes.

    Exiger enhanced UFLPA solution, checked 5 November 2026
    Third-party due diligence workflowDocumented by vendor

    The due diligence page lists sanctions, modern slavery, adverse media and other checks, risk profiles organised by risk event, configurable rules and a record of decisions. That page mentions analysts only in a customer quotation, but the third-party risk management page, re-read on 5 November 2026, states that Exiger's due diligence researchers examine public records, corporate affiliations, litigation and reputation when a relationship warrants deeper review, and that SmartSource adds discreet source inquiries. Confirm what a modern slavery finding looks like in a record, which reviews Exiger's researchers perform and whether they are included in the quote.

    Exiger due diligence solutions, checked 5 November 2026Exiger third-party risk management, checked 5 November 2026
    Product-level modern slavery data and integrationsDepends on scope

    The risk and compliance page describes product-aware datasets linking products to input-level origin, facilities and owners, and an API-first approach with native ERP, source-to-pay and case system integrations. Verify which integrations are available for your systems and which data modules are in your contract.

    Exiger risk and compliance, checked 5 November 2026
    Security certificationsDocumented by vendor

    The risk and compliance page states FedRAMP Moderate authorisation, ISO 27001 and SOC 2 Type 2. The vendor trust page, read on 5 November 2026, lists SOC 2 Type 2, ISO/IEC 27001:2022, NIST CSF, CMMC, DoD IL4 and FedRAMP High, and does not list FedRAMP Moderate. Request current reports and confirm which authorisation and deployment cover the service you would buy.

    Exiger risk and compliance, checked 5 November 2026Exiger trust center, checked 5 November 2026
    Third-party onboarding and continuous monitoringDocumented by vendor

    Re-read on 5 November 2026, the third-party risk management page describes assessing relationships at onboarding with questionnaires and review steps configured to each third party's criticality, recording the assessment and monitoring for changes that call for further diligence or remediation. It lists forced labour and modern slavery among the human rights concerns assessed alongside other third-party risks. The page no longer mentions offboarding or real-time risk ratings; conditional questionnaire workflows are described in the modern slavery article. Ask to see how a relationship is closed and how a risk change triggers a review.

    Exiger third-party risk management, checked 5 November 2026Modern slavery tools article, checked 5 November 2026
    Transshipment and trade-origin detectionDocumented by vendor

    The article describes rebuilding trade routes from shipment records and linking shipments to beneficial owners and forced labour risk. Test it with your own shipment data.

    Exiger transshipment intelligence article, checked 5 November 2026

    Exiger pricing

    Quote-based

    Separate pricing recheck date not recorded. Confirm current pricing with the vendor.

    Which product scope should the quote cover?

    Supply chain risk, third-party risk and due diligence on the 1Exiger platform; software supply chain security is a separate product.

    Ask the vendor to identify the product, region, modules, billing unit, contract term and included services in writing.

    Public procurement records

    Amounts are as published in each document and are not list prices for the general market. A G-Cloud amount is the supplier's price to UK public buyers on that framework and not a general price list; an award or order amount is a total for a scope that can include licences and services and several years. No unit price is derived from any total. A record can be for another product from the same supplier, so check what was priced in each one. Records read .

    What these records cannot tell youAll records as CSV (CC BY 4.0)

    1. US federal award record (USAspending.gov; delivery order under IDV NNG15SC03B)

      Recipient:
      CARAHSOFT TECHNOLOGY CORP (recipient; not the software maker)
      Period from:
      Buyer:
      Nuclear Regulatory Commission, United States
      What was priced:
      Description: EXIGER THIRD PARTY AND SUPPLY CHAIN RISK MANAGEMENT (SCRM) CONTRACT RENEWAL (BASE AND 4 OPTION YEARS)
      Amount as stated:
      Obligated $284,784.19; potential award amount $1,641,705.69
      Units:
      None stated
      Term:
      1 Oct 2026 to 30 Sep 2027; potential end 30 Sep 2030
    2. US federal award record (USAspending.gov; delivery order under IDV NNG15SD19B)

      Recipient:
      ALVAREZ LLC (recipient; not the software maker)
      Period from:
      Buyer:
      U.S. Coast Guard (Department of Homeland Security), United States
      What was priced:
      Description: EXIGER SOFTWARE AS A SERVICE FOR RESEARCH DEVELOPMENT & ACQUISITIONS SUPPLY CHAIN RISK MANAGEMENT (RDA/SCRM) TOOL
      Amount as stated:
      Obligated $331,730.81; potential award amount $1,463,762.22
      Units:
      None stated
      Term:
      4 Sep 2026 to 14 Sep 2027; potential end 14 Sep 2030
    3. US federal award record (USAspending.gov; definitive contract)

      Recipient:
      CONVERGENT SOLUTIONS, INC. (recipient; not the software maker)
      Period from:
      Buyer:
      Department of the Army (Department of Defense), United States
      What was priced:
      Description: 1 EXIGER SUBSCRIPTION FOR SUPPLY CHAIN ORCHESTRATION AND MONITORING FOR THE U.S. ARMY MATERIEL COMMAND; negotiated proposal; 1 offer
      Amount as stated:
      Obligated $10,543,633.90
      Units:
      1 subscription
      Term:
      30 Oct 2025 to 25 Sep 2026

    Offline work and integrations

    Not applicable in the usual sense: Exiger is a web platform for supplier risk assessment and reporting, and no offline or mobile field mode is documented on the reviewed pages.

    What we could not verify

    2 depend on scope · 1 note

    Demo script

    Proposed demo: bill of materials to evidenced forced labour flag

    1. Provide a sample product bill of materials and supplier list covering at least three tiers.
    2. Review the map, noting which tiers and links are inferred rather than confirmed.
    3. Open a flagged entity, inspect its evidence and record a reviewer decision.
    4. Trace the finding to an action and to the statement or disclosure it would support; export the audit record.

    Proposed demo: third-party onboarding with continuous monitoring

    1. Onboard a test third party through a workflow that includes forced labour and adverse media checks.
    2. Review the resulting risk profile and note which risk events contribute to the rating.
    3. Ask the vendor to show a later risk change raising a monitoring alert.
    4. Ask the vendor to show how the relationship is closed or offboarded, then export the full decision record for audit.

    Ask the vendor to show you

    1. Which data do suppliers need to provide, and what is scored from spend and supplier names alone?
    2. How does the platform capture signals that contradict a supplier's own questionnaire answers?
    3. How is a finding linked to a remediation action and to the sentence in the published statement?
    4. Which jurisdictions' reporting criteria are mapped (UK, Australia, Canada, EU), and who maintains that mapping?

    Checks specific to this product

    Sub-tier depth on your own products:
    Supply a sample bill of materials and ask the vendor to map it. Record the tiers reached, how many entities are resolved and which links are inferred. Keep the output for comparison with supplier-confirmed data.
    Use demo checklist

    Sources and change log

    14 sources, checked
    • : Re-checked all eleven cited sources on 5 November 2026; the trust page needed a browser read. Exiger has rewritten its third-party risk management page: it no longer mentions offboarding or real-time risk ratings, and it now says Exiger's due diligence researchers carry out deeper reviews, so the onboarding and due diligence capabilities and the offboarding demo step were reworded. The trust page lists FedRAMP High, DoD IL4 and CMMC but not FedRAMP Moderate, which the risk and compliance page still states; DoD IL4 was added and the FedRAMP Moderate entry is now attributed to that page. Added the laws listed on Exiger's ESG risk page, a 10 September 2026 press release naming Carlyle, Insight Partners and JMI Equity as investors, and the named integrations and hosting subprocessors. Pricing is still not published and no trial is offered. The forced labour mapping, nth-tier, UFLPA, product data and transshipment capabilities were re-confirmed.

    Compare with

    Drawn from the profiles behind the Alternatives list above: most category tags shared with Exiger first, then the closest overlap in documented capability names, then A to Z. Ratings, search demand and sponsorship are not used; rows are shown A to Z.

    • Fair Supply

      Shared category tags: 3 (Modern Slavery, Supplier Due Diligence, others).

      Same: scope, offline, price and trial.

    • Informed 365

      Shared category tags: 3 (Modern Slavery, Supplier Due Diligence, others).

      Same: scope, offline, price and trial.

    • IntegrityNext

      Shared category tags: 3 (Modern Slavery, Supplier Due Diligence, others).

      Same: scope, offline, price and trial.

      Side by side: Exiger and IntegrityNext
    All Exiger alternatives

    Reviews

    This site does not currently collect reader reviews. Star ratings and review counts from the old catalog are not shown: no source for them was recorded.