    qmsWrapper

    qmsWrapper's pages describe a quality system built around quality events, which are triaged by risk into nonconformance or CAPA records and linked to change, deviation, complaint and risk work. It is sold in three levels: Foundation (forms, documents, e-signatures, training), Lifecycle (CAPA, change, risk, supplier) and Vigilance (technical file, post-market surveillance, audit evidence). The technical overview also lists an audit trail per entity and an AI findings inbox with human approval.

    Evidence: Researched profile

    Built from vendor sources checked ; AI-assisted drafting. Documentation review, not a hands-on test. How pages are made

    Who is qmsWrapper for?

    Small and mid-sized medical device companies replacing paper or spreadsheet records and wanting linked design, risk, CAPA and post-market records. An API, single sign-on and offline use are not described on the vendor pages, and the pages give differing statements on SOC 2 and ISO 27001, so neither is claimed. Prices for Lifecycle and Vigilance are not shown. The standards wording describes alignment, not software certification.

    Watch for: An API, offline use and SOC 2 / ISO 27001 status are unclear.

    Published price: From €3,499 per year for Level 1 - Foundation. Sources checked .

    Product tour

    Vendor visuals—not a QHSEtech hands-on test.

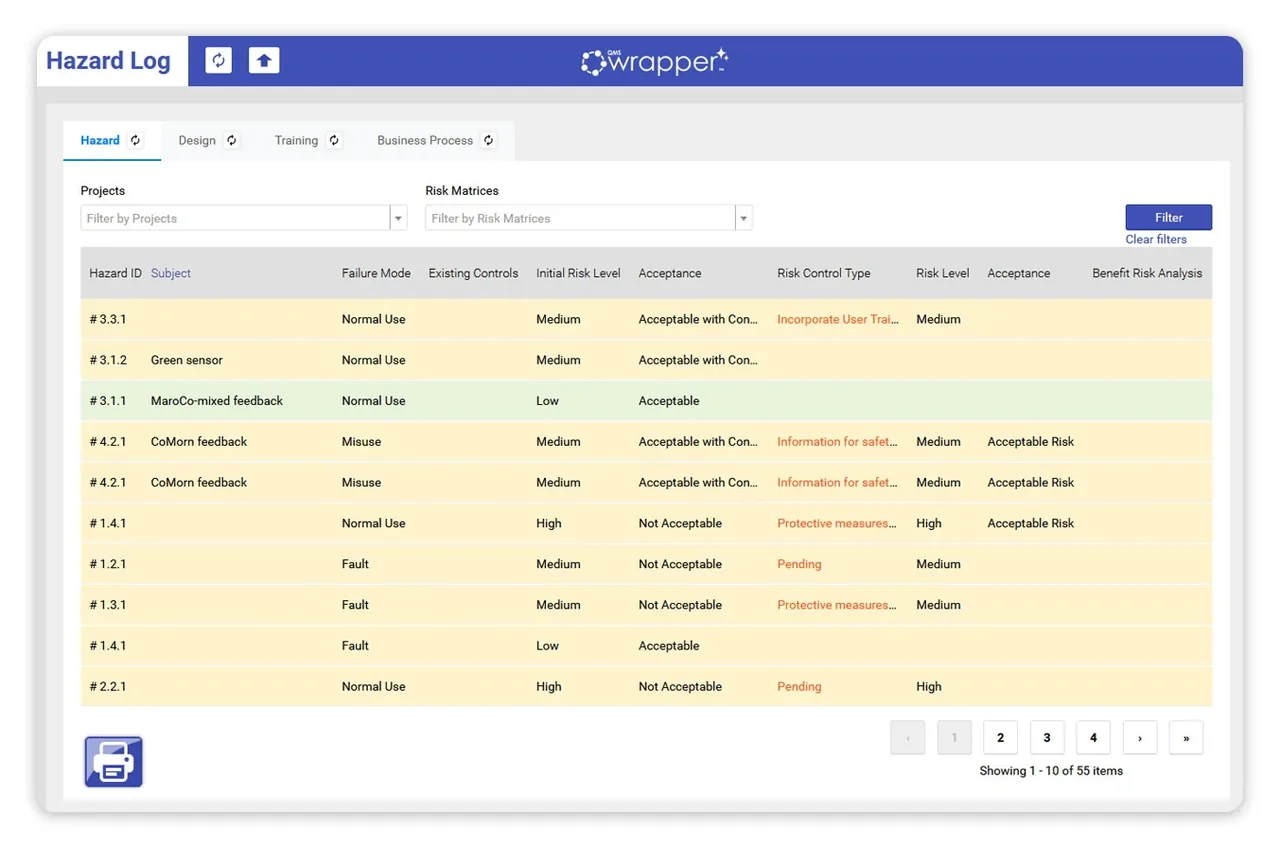
    qmsWrapper Hazard Log screen with a table of hazards, risk levels, acceptance status and risk control types, with pagination

    Hazard log table for ISO 14971 risk management

    Source
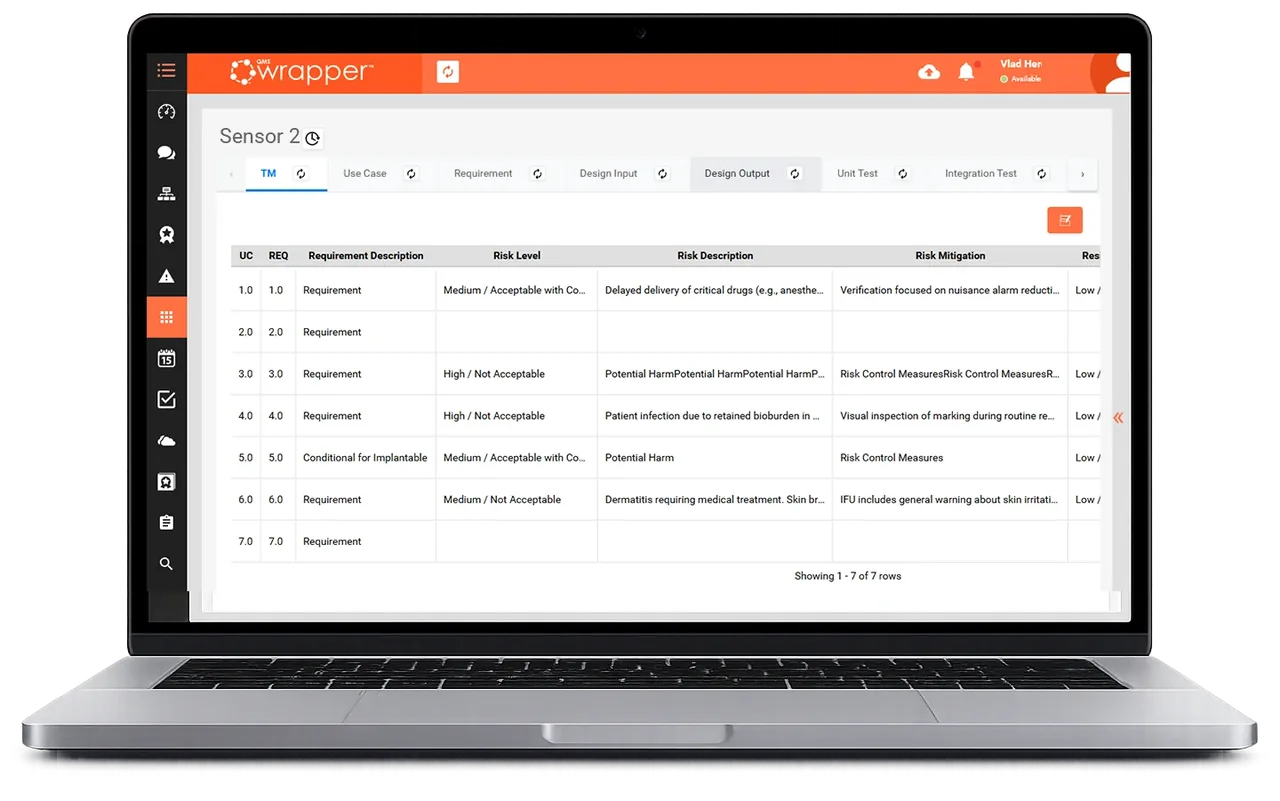
    Laptop showing a qmsWrapper traceability matrix table with requirements, risk levels, risk descriptions and mitigations

    Design traceability matrix linking requirements and risks

    Source

    Capabilities and scope

    qmsWrapper is an electronic quality management system for medical device, SaMD and in-vitro diagnostic teams. The site footer says it is a division of UVA Research Corp. of Markham, Ontario, Canada, and the vendor states a figure of 500+ medtech teams. This profile covers quality management only, not EHS or occupational safety. ISO 13485, FDA 21 CFR Part 820, 21 CFR Part 11 and EU MDR are named as frameworks the workflows align with; no certificate for the software is named. Document control, e-signatures, training, CAPA, nonconformance, change, complaints, risk, design traceability, supplier, audit and post-market records for medical device quality systems.

    qmsWrapper capabilities, evidence status and source links
    CapabilityEvidenceScope and source
    Quality events, CAPA and nonconformanceDocumented by vendor

    The CAPA page describes events classified by risk and escalated only when justified, nonconformance as its own record, a lighter log and an eight-stage lifecycle with independent QA sign-off.

    qmsWrapper CAPA and nonconformance page, checked 2 October 2026qmsWrapper technical overview, checked 2 October 2026
    Document control and electronic signaturesDocumented by vendor

    The pages describe versioned documents, approval chains and signatures linked to a document version, user, role and time, described as aligned with, or compliant with, 21 CFR Part 11. No certification is named.

    qmsWrapper document control and e-signatures page, checked 2 October 2026qmsWrapper technical overview, checked 2 October 2026
    ISO 14971 risk management and hazard logsDocumented by vendor

    The risk page describes hazard logs, risk evaluation, controls and residual risk linked to requirements and design elements, with events triggering re-evaluation.

    qmsWrapper ISO 14971 risk management page, checked 2 October 2026qmsWrapper home page, checked 2 October 2026
    Design control and traceability matrixDocumented by vendor

    The pages describe linked user needs, requirements, risks, inputs, outputs, validation and verification records, and a design history file and technical file structure.

    qmsWrapper design control traceability page, checked 2 October 2026qmsWrapper technical overview, checked 2 October 2026
    Audit managementDocumented by vendor

    The audit page describes planning and running internal, external and supplier audits with checklists, and converting findings into events, CAPA and actions.

    qmsWrapper audit module page, checked 2 October 2026

    More capability notes

    6 additional areas. Status describes reviewed sources, not hands-on performance.

    qmsWrapper pricing

    Three levels; Level 1 - Foundation shown per year, Lifecycle and Vigilance priced on request

    The subscription terms page, the home page and the demo page show one amount: pricing starts at €3,499 per year for Level 1 - Foundation. Lifecycle is described as priced on company size and Vigilance as priced on scope, with no amount shown for either. The home page says there are no per-seat licences and that pricing follows company size, not user count. A trial is not described on the vendor pages, though a third-party listing mentions one.

    Separate pricing recheck date not recorded. Confirm current pricing with the vendor.

    Offline work and integrations

    Offline use and a mobile app are not described on the reviewed pages.

    What we could not verify

    1 not verified · 4 depend on scope · 2 notes
    • Not verified in the sources: Integrations and API.
    • Depends on plan or configuration: Post-market vigilance and EUDAMED records; Complaints, supplier and training records; Configurable forms and workflows; Validation documentation and security.
    • VAT, billing terms and company-size bands are not stated; full terms are agreed at order placement, and no refunds are given once access is activated, except where the law requires.
    • Prices for the two higher levels are not shown.

    Demo script

    Proposed demo: complaint to CAPA and risk update

    1. Log a customer complaint and show it becoming a quality event.
    2. Escalate it to CAPA and step through investigation, approval and effectiveness with e-signatures.
    3. Show the linked hazard log update and any design traceability change.
    4. Open the audit trail and an audit finding that references the CAPA.
    5. Export the records an inspector would request.

    Ask the vendor to show you

    1. Which level contains each module we need, and what is the written price for our company size?
    2. Show a complaint becoming a CAPA with the risk record updated and each step in the audit trail.
    Use demo checklist

    Sources

    10 sources, checked

    Reviews on qhsetech.com

    Reviews may be filed under other names

    Also recorded as QMSWrapper. Older entries under a previous name may describe a different release or owner.

    Star ratings and review counts from the old catalog are not shown: no source for them was recorded.