QHSEtech

    Onspring

    Onspring links enterprise risk, incident handling and audit work through configurable applications. Risk registers and remediation provide governance context for QHSE teams, while internal audit supports planning, evidence and findings. Fit depends on the workflows and administration capacity of the organization, especially where dedicated field-safety functions are required.

    Evidence: Researched profile

    Built from vendor sources checked ; AI-assisted drafting. Documentation review, not a hands-on test. How pages are made

    Who is Onspring for?

    Risk, compliance and internal audit teams coordinating registers, evidence and remediation across business units. A quote must combine the licensing model, chosen products, platform level, environments, storage, API/SMS allowances, implementation and any third-party data subscriptions. Product licensing's unlimited-use statement applies to employee users for selected products; it does not establish unlimited external-user access or access to every product. Onspring AI requires a separate licence and the pricing page limits it to Silver or higher; AI summaries and automated actions remain subject to prompt, data, permission and human-review controls. Native integrations can depend on separately purchased third-party content, and a logo or API-planning worksheet is not proof that a production connector is included. Portal access, public workflows and external collaboration require explicit permission and licensing validation. FedRAMP wording applies to Onspring GovCloud and must not be transferred automatically to the standard service. Real-time dashboards reflect the data and refresh process configured; they are not proof of safety-critical monitoring. Offline capture, mobile synchronization, inspections, permit-to-work, chemical management and other specialist EHS workflows remain unverified.

    Worth considering when governance, risk and audit coordination are the main problem. Compare platform, application and administration costs together. For field-safety requirements, require direct evidence of task coverage before assigning value to the wider GRC suite.

    Sources checked .

    Product tour

    Vendor visuals—not a QHSEtech hands-on test.

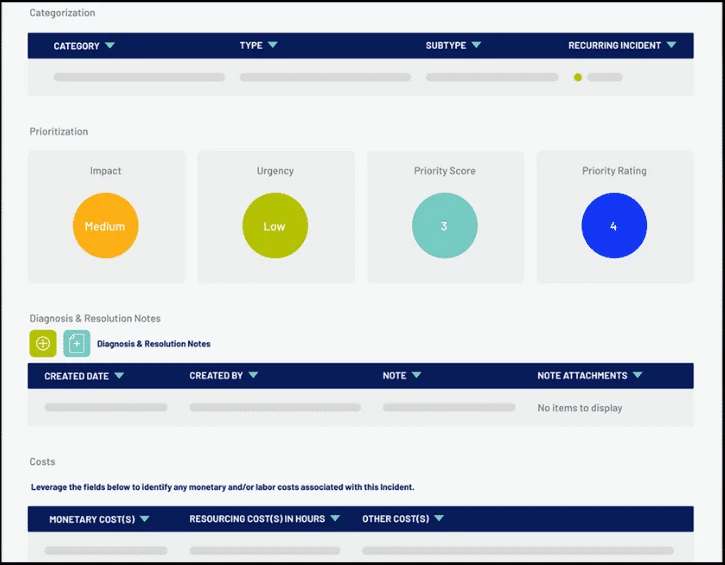
    Incident record with category fields, impact and urgency indicators, resolution notes and cost tables

    Incident prioritization and resolution notes

    Source
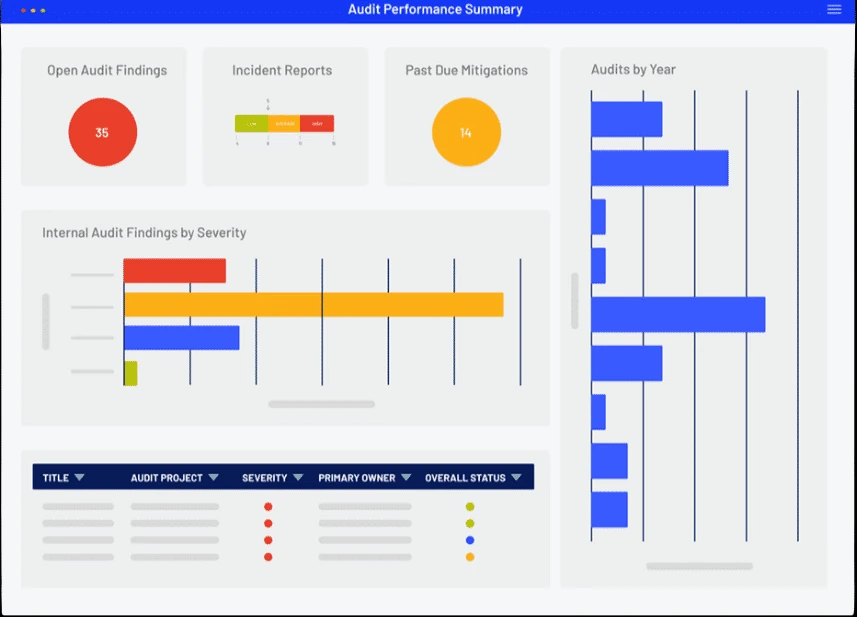
    Audit dashboard with open findings, past due mitigations, findings by severity and audits by year

    Internal audit performance summary

    Source

    Capabilities and scope

    Onspring is a configurable no-code governance, risk and compliance platform sold through separately selected user or product licensing and Bronze, Silver, Gold or Platinum platform levels. Onspring AI is an optional add-on and requires its own licence.

    Onspring capabilities, evidence status and source links
    CapabilityEvidenceScope and source
    Incident intake, routing and escalationDocumented by vendor

    The incident product documents customizable intake, severity or impact-based workflow, notifications, escalation and response playbooks. Buyers must configure fields, thresholds, ownership and response rules for their own governance model.

    Enterprise incident workflows
    Root-cause and corrective-action trackingDocumented by vendor

    Onspring documents root-cause analysis, resolution steps, closure verification and incident trend reporting. This is a configurable enterprise incident workflow, not proof of a prebuilt regulatory safety-investigation method.

    Enterprise incident workflows
    Risk register and mitigation managementDocumented by vendor

    The risk product documents centralized and hierarchical registers, assessments, causes and interdependencies, mitigation measures, controls, barriers, acceptance, KRIs and overdue-action notifications. Scoring and approvals must be configured to the buyer's method.

    Risk assessment and register
    Internal-audit planning and workpapersDocumented by vendor

    The audit product documents audit-universe planning, resource and budget tracking, workpapers, multi-level sign-off, findings and report issuance. Validate methodology, templates and retained change history with a sample audit.

    Internal audit workflow
    Audit evidence and external collaborationDepends on scope

    Onspring documents surveys, evidence requests and secure external-auditor portal access. Confirm Portal/product entitlement, external-user licensing, upload controls and record-level permissions.

    Internal audit workflowPortal and external collaboration
    No-code data model and task automationDocumented by vendor

    The platform documents data references, formulas, tasks, shared lists and multi-record creation. No-code reduces coding dependency but still requires design ownership, change control, testing and administrator capacity.

    No-code platform feature overview
    Rules-based workflows and approvalsDocumented by vendor

    Visual workflows can route internal or external assessments, tasks, notifications and approvals using conditions. Public versus private visibility and email, SMS or Slack actions must be tested against least-privilege requirements.

    Rules-based dynamic workflows
    Surveys and attestationsDocumented by vendor

    The platform overview documents scheduled or ad hoc assessments, attestations and compliance questionnaires. Confirm participant licensing, authentication, reminders, evidence requirements and reopening rules.

    No-code platform feature overview
    Dashboards, reports and document exportsDocumented by vendor

    Onspring documents role-oriented dashboards, live drill-down reports and Word or PDF output. 'Real-time' depends on the configured data inputs and does not establish safety-critical monitoring or an immutable regulatory report.

    No-code platform feature overviewReal-time reporting and exports
    Automated messages, alerts and scheduled reportsDepends on scope

    Business rules can trigger notifications and scheduled reports; the workflow and overview pages name email, SMS and Slack channels. SMS allowances vary by platform level and channel delivery, escalation and failure handling require validation.

    Automated messages, alerts and reportsCommercial licensing and platform tiersRules-based dynamic workflowsNo-code platform feature overview
    Integrations and APIDepends on scope

    Onspring lists native integrations and provides API-planning material. Some data connectors require third-party subscriptions; confirm API allowance, authentication, supported direction, error handling and maintenance for each interface.

    Integrations and API planningCommercial licensing and platform tiers
    Data consolidation and relationshipsDocumented by vendor

    The platform documents importing data, relating records to workflows, reports or people, and aggregating them into dashboards. Source ownership, matching, refresh, duplicate and reconciliation controls remain implementation responsibilities.

    Data import, relationships and consolidation

    More capability notes

    2 additional areas. Status describes reviewed sources, not hands-on performance.

    Also watch for: No numeric subscription price published on the reviewed pricing page. Platform tiers do not themselves include user or product licences.

    Onspring pricing

    Custom quote

    Pricing is not publicly available as a numeric subscription, contact vendor. Onspring publishes user-based, product-based and hybrid licensing. Bronze, Silver, Gold and Platinum platform levels are separate from user or product licences. Request implementation, environments, API capacity, storage, third-party subscriptions, currency and renewal terms.

    Pricing sources checked : Selected sources checked; no starting price recorded. The pricing page publishes licensing structure without numeric rates. A demo is not evidence of a free trial.

    Which product scope should the quote cover?

    Configurable enterprise GRC platform covering incident, risk and internal-audit workflows, analytics, surveys, messaging, portals and integrations; specialist operational EHS and offline field workflows require separate proof.

    Ask the vendor to identify the product, region, modules, billing unit, contract term and included services in writing.

    Offline work and integrations

    The reviewed Onspring sources do not establish offline form capture or synchronization.

    What we could not verify

    1 not verified · 4 depend on scope · 2 notes
    • Not verified in the sources: Specialist frontline EHS and offline field coverage.
    • Depends on plan or configuration: Audit evidence and external collaboration; Automated messages, alerts and scheduled reports; Integrations and API; Onspring AI.
    • Incident, enterprise risk and internal audit products are relevant to QHSE governance, but the reviewed material does not establish a specialist frontline EHS suite, disconnected inspection app, permit-to-work system or chemical inventory product.
    • Treat disconnected field work as unverified and demonstrate the intended workflow before including it in a shortlist requirement match.

    Demo script

    Demo exercise: incident linked to risk treatment

    1. Submit an operational incident through a restricted intake form with impact, evidence and owner.
    2. Trigger severity-based routing, notifications and an overdue escalation.
    3. Complete root-cause analysis and link corrective actions to the relevant risk, control and treatment plan.
    4. Verify closure approval, retained communications, dashboard updates and exportable audit history.

    Demo exercise: audit evidence and external access

    1. Plan a sample audit, assign resources, budget and workpapers, and apply multi-level sign-off.
    2. Send one evidence request to a process owner and one to an external auditor through the proposed access method.
    3. Test that each participant can see only the intended audit, documents and workflow actions.
    4. Convert an exception to a finding and remediation action, then issue and export the final report.

    Demo exercise: no-code change governance

    1. Clone a representative incident or audit workflow into the proposed non-production environment.
    2. Add a field, conditional approval, notification and dashboard metric without developer code.
    3. Run positive, negative, permission and regression cases with representative roles.
    4. Promote the approved configuration and show version, owner, approval and rollback evidence.

    Ask the vendor to show you

    1. Which named Onspring products, user groups and employee or external participant types are included in the quote?
    2. Why is user, product or hybrid licensing the best fit, and which access scenarios would incur additional licences?
    3. Which Bronze, Silver, Gold or Platinum allowances do we need for storage, API calls, environments, SMS, firewall changes, training and support?
    4. Which implementation work is included under the chosen licensing model, and who owns future no-code administration and regression testing?
    5. Which integrations are native and included, which require third-party subscriptions, and which need API development and ongoing maintenance?
    6. Does external-auditor or supplier access require Portal or another entitlement, and how are least-privilege and record-level permissions enforced?
    Use demo checklist

    Questions the sources answer

    Is Onspring a dedicated EHS inspection platform?

    The reviewed official material positions Onspring as a configurable GRC platform with incident, risk and audit products. Do not infer offline inspections, permits, chemical management or occupational-health functionality without a task-specific demonstration and scoped configuration.

    How is Onspring licensed?

    Onspring publishes user, product and hybrid licensing, selected separately from Bronze, Silver, Gold or Platinum platform levels. Numeric prices require a quote, and the final scope should include products, participant types, environments, storage, API/SMS allowances and support.

    Is implementation included?

    The pricing page says implementation is included depending on the licensing model. Require a statement of work defining configuration, migration, integrations, training, acceptance criteria and post-launch administration.

    Is Onspring AI included?

    No assumption should be made. Onspring describes AI as an optional add-on requiring a licence, and its pricing page says it is available with Silver or higher. Define permitted use cases, human review and audit requirements before enabling it.

    Are all listed integrations included?

    Not necessarily. Onspring lists integrations and API planning, while pricing notes third-party subscriptions may be required for vendor-risk data connectors. Confirm each production interface, commercial dependency and support owner.

    Can external auditors or suppliers collaborate in Onspring?

    The audit and Portal pages describe external collaboration, evidence submission and restricted workflow access. Confirm Portal/product entitlement, external-user licensing, authentication and record-level permissions in the proposed design.

    Does FedRAMP apply to every Onspring deployment?

    No. The security page associates FedRAMP certification with Onspring GovCloud. Obtain assurance documents for the exact service and hosting option being purchased.

    Can Onspring connect audit findings with risk management?

    The platform and product pages document related records, audit findings, controls, risks and remediation. Demonstrate the cross-product linkage, permissions and reporting using the exact licensed products before agreeing scope.

    Sources

    13 sources, checked

    Compare with

    Drawn from the profiles behind the Alternatives list above: most category tags shared with Onspring first, then the closest overlap in documented capability names, then A to Z. Ratings, search demand and sponsorship are not used; rows are shown A to Z.

    • Riskonnect

      Shared category tags: 3 (Risk Management, Incident Management, others).

      Same: scope, offline, price and trial.

      Side by side: Onspring and Riskonnect
    • RLDatix

      Shared category tags: 3 (Risk Management, Incident Management, others).

      Same: scope, offline, price and trial.

    All Onspring alternatives

    Reviews on qhsetech.com

    Star ratings and review counts from the old catalog are not shown: no source for them was recorded.